AI task force corporate risks guide for innovation
"The management of risks for medical devices is described by the International Organization for Standardization (ISO) in ISO 14971:2019, a product safety standard."
Establishing an AI task force corporate risks strategy requires balancing rapid innovation against potential operational or legal fallout. This guide examines the dangers of rapid adoption, the necessity of structured planning, and how to manage the fallout of specialized units.
Key takeaways include the importance of value-driven mitigation, the necessity of a formal risk treatment plan, and the specific dangers of resource mismanagement.
What are the main risks to my company's AI task force?
At midnight in the empty office, a cold sweat broke across my skin as I contemplated the failure of our AI task force. I stood in the silent boardroom at midnight, feeling a cold sweat as I realized how much our task could jeopardize the company.
Walking into a boardroom to discuss a new technology unit often involves navigating unpredictable variables. An AI task force corporate risks profile typically includes legal liability, data security breaches, and operational instability.
Without a clear framework, these specialized units can create more friction than efficiency.
The International Organization for Standardization (ISO) identifies the following principles for risk management: Create value – resources expended to mitigate risk should be less than the consequence of inaction.
If the cost of managing the task force exceeds the value it generates, the initiative fails to meet foundational business principles. Managing AI risks firms must ensure that the investment in oversight stays within reasonable bounds.
The primary risks involve misalignment between technical capabilities and strategic goals, as well as potential data privacy breaches. In this sequence, the first risk is the most critical.
How should an organization structure its response? AI task force corporate risks
I sat hunched over the desk at dawn, feeling the sting of exhaustion while I mapped out the response to our task.
Reviewing a spreadsheet of potential vulnerabilities requires a systematic approach to prevent chaos. AI adoption business risks can be mitigated by following established international frameworks for assessment and response.
A structured sequence ensures that no single point of failure collapses the entire project.
According to ISO/IEC 27001, the stage immediately after completion of the risk assessment phase consists of preparing a Risk Treatment Plan, which should document the decisions about how each of the identified risks should be handled.
This documentation ensures that every identified vulnerability has a designated owner and a specific mitigation strategy.
- Conduct a comprehensive risk assessment to identify all potential technical and legal vulnerabilities. 2. Develop a Risk Treatment Plan to document how each identified risk will be handled. 3. Execute the plan while continuously monitoring for new emerging threats.
I once sat in a planning session where we realized our initial assessment lacked a clear treatment path, nearly leading to a total project stall.
- Define the scope of authority for the task force.
- Establish cross-departmental communication channels.
- Set clear reporting lines to executive leadership.
What are the dangers of expanding my tasks?
Expanding a specialized unit too quickly can lead to oversight failures or legal entanglement. Task expansion AI dangers often manifest when a group's scope grows beyond its ability to maintain control or compliance.
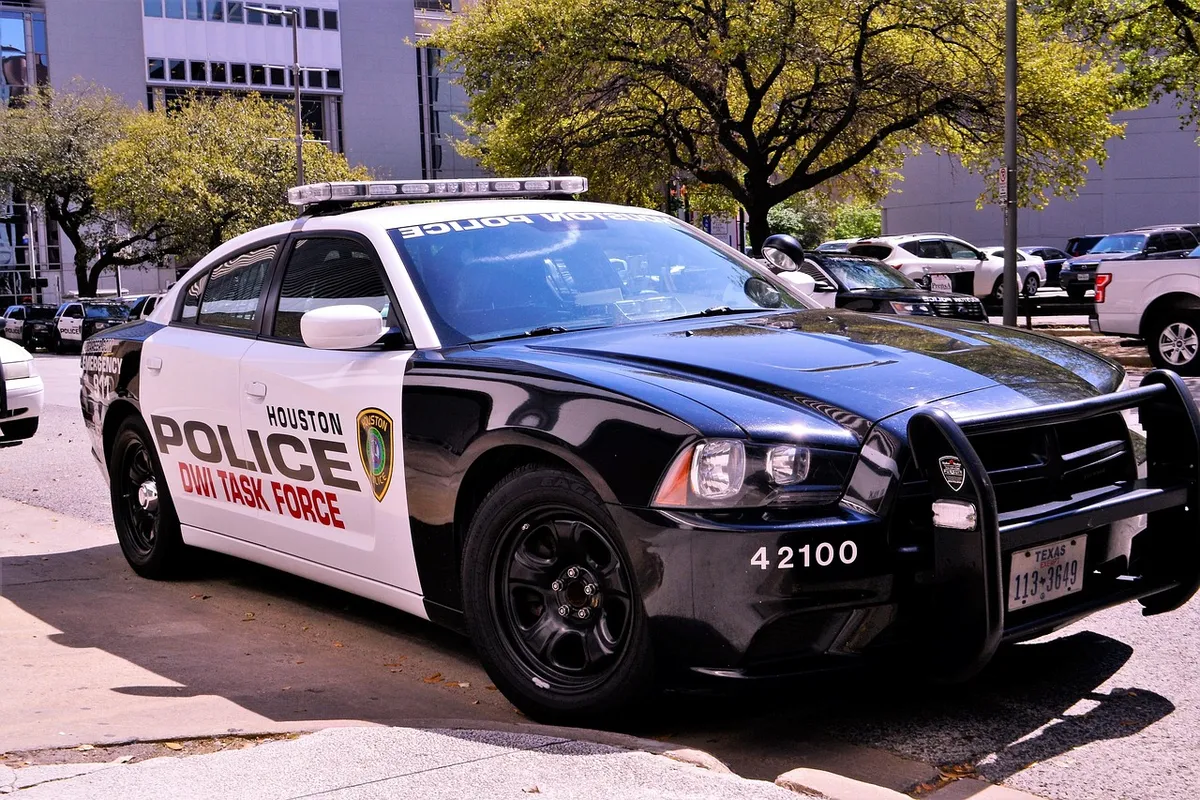
According to the Tennessee Bureau of Investigation, as of July 2026, the Tennessee Bureau of Investigation (TBI) was investigating eight use-of-force incidents involving task force members.
As of July 2026, the Tennessee Bureau of Investigation (TBI) was investigating eight use-of-force incidents involving task force members. This historical example illustrates how specialized units can face intense scrutiny when their actions fall outside expected operational boundaries.
Expanding the scope too quickly can lead to resource depletion and diluted focus. In this sequence, the second danger is the most significant.
How can firms manage AI task force risks during implementation?
Setting up a new department involves much more than just hiring technical experts. Mitigating AI task force risks requires a balance between aggressive development and conservative safety protocols.
The management of risks for medical devices is described by the International Organization for Standardization (ISO) in ISO 14971:2019, Medical Devices—The application of risk management to medical devices, a product safety standard.
While this specific standard focuses on medical hardware, the principle of applying rigorous risk management to specialized technology is universal.
| Phase | Action | Goal |
|---|---|---|
| Assessment | Identify vulnerabilities | Documented risk profile |
| Treatment | Execute plans | Risk mitigation |
Firms should implement continuous monitoring and iterative feedback loops to catch errors early. In this sequence, the first step is the most vital.
What are the limitations of risk management?
Looking at a mitigation strategy through a narrow lens can hide broader systemic issues. An AI risk response strategies approach must account for the fact that no plan is entirely foolproof.
A limitation of any risk management framework is that it cannot account for every unpredictable human or technical variable.
For example, while a plan may address known vulnerabilities, it may not account for the sudden shifting of legal landscapes or unexpected behavioral changes within the task force.
Risk management cannot eliminate all uncertainty, as emerging technologies often outpace existing frameworks. In this sequence, the first limitation is the most fundamental.
The same subject is also called AI task force dangers.
The same subject is also called AI task planning issues.
Mitigating AI task force risks
Related
Comments 0